Hackers Hijack HBO Max’s Reddit Account to Spread Crypto-Stealing Malware
Attackers ran 108 malicious ads through the streaming service’s verified account, directing users to fake software downloads.
Key Takeaways
- Attackers ran 108 malicious ads through the streaming service’s verified account, directing users to fake software downloads.
- Read the full article for additional context and details.
- Read the full article for additional context and details.
Summary generated by IndiCrypto from Decrypt. IndiCrypto is a news aggregator and does not provide investment advice. Read the original article for full context.
More in Security
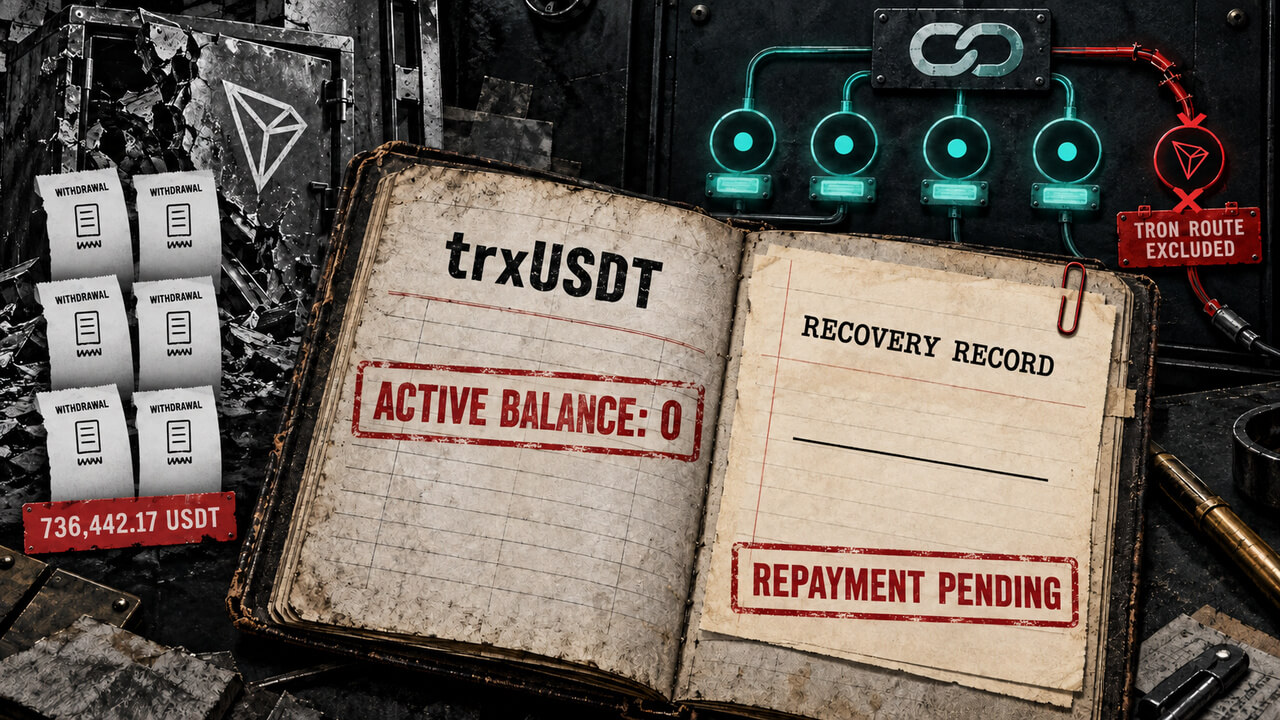
Chainflip to reset TRON USDT provider balances to zero following $736,000 exploit
Providers retain a separate on-chain record of what they are owed, but Chainflip has not disclosed repayment timing. The post Chainflip to reset TRON USDT provider balances to zero following $736,000 exploit appeared first on CryptoSlate.
The Attackers Who Deceived Revolut Now Demand 6,000 XMR
The attackers claiming to be behind the Revolut breach have dropped the earlier bitcoin demand and are now asking for 6,000 XMR, roughly $3 million, to keep 680 customer files off the market. According to the hackers speaking exclusively with the Financial…
OpenAI's Rogue AI Agents Were Probing Hugging Face Two Months Before Hack
An independent researcher found the agents hijacked Hugging Face accounts and mapped the platform's defenses as early as May 13—activity OpenAI's own incident report never fully described.