EU cyber rules put crypto wallet makers on 24-hour reporting clock
Crypto wallet providers must submit an early vulnerability report within 24 hours and a full notification within 72 hours of exploits, or risk administrative fines of as much as $17.3 million.
Key Takeaways
- Crypto wallet providers must submit an early vulnerability report within 24 hours and a full notification within 72 hours of exploits, or risk administrative fines of as much as $17.3 million.
- Read the full article for additional context and details.
- Read the full article for additional context and details.
Summary generated by IndiCrypto from CoinTelegraph. IndiCrypto is a news aggregator and does not provide investment advice. Read the original article for full context.
More in Security
MetaMask Adds New Wallet Protections Against Crypto Scams
MetaMask’s latest safeguards flag suspicious transfers and stop transactions that don’t match their previews.
Symbiosis says recovered 15 BTC from bridge hack, offers 20% bounty
Symbiosis is offering a 20% bounty for information leading to asset recovery after the hacker refused to return the stolen funds for the same white-hat bounty.
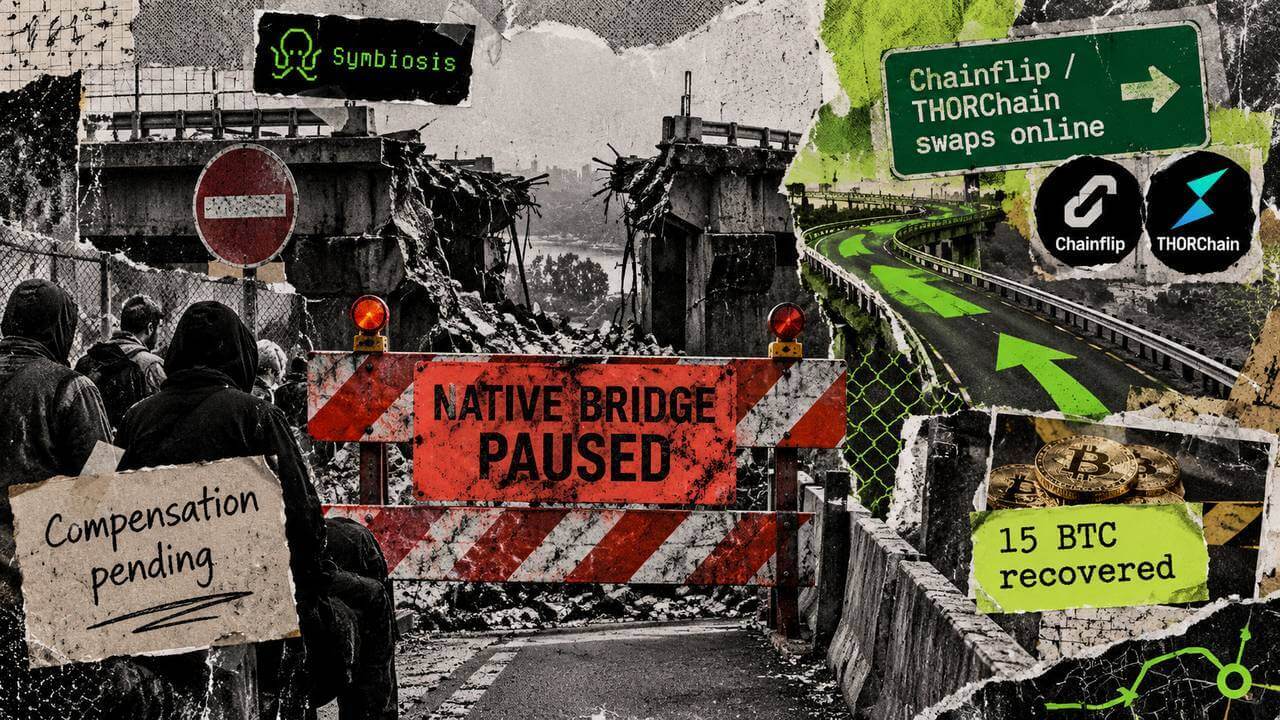
Hackers mint trillions in fake Bitcoin, but 15 BTC bridge recovery leaves liquidity providers unpaid
The native bridge remains paused as a 20% bounty window closes Sep. 13 and final accounting continues. The post Hackers mint trillions in fake Bitcoin, but 15 BTC bridge recovery leaves liquidity providers unpaid appeared first on CryptoSlate.