Phishing Campaign Targets Crypto Users Through Fake Wallet Apps
Security researchers have identified an active phishing campaign that distributes counterfeit cryptocurrency wallet applications engineered to steal users’ recovery phrases. The fake apps closely imitate the branding of popular wallets and spread through unofficial download links, search ads, and social media messages. Researchers recommend downloading wallet software only from official websites or verified app-store listings, and never entering a recovery phrase into any app or web form.
Key Takeaways
- Fake wallet apps aim to steal recovery phrases.
- Download wallets only from official, verified sources.
- Never enter a seed phrase into an app or website.
Summary generated by IndiCrypto from BeInCrypto. IndiCrypto is a news aggregator and does not provide investment advice. Read the original article for full context.
More in Security
White-Hat Hackers Route Coldcard Exploit Bitcoin Into 'Recovery Trust'
Galaxy Research says white-hat actors consolidated coins tied to the exploit into a fresh address tagged for a "Crypto Recovery Trust," though the funds represent just 2.8% of the total haul.
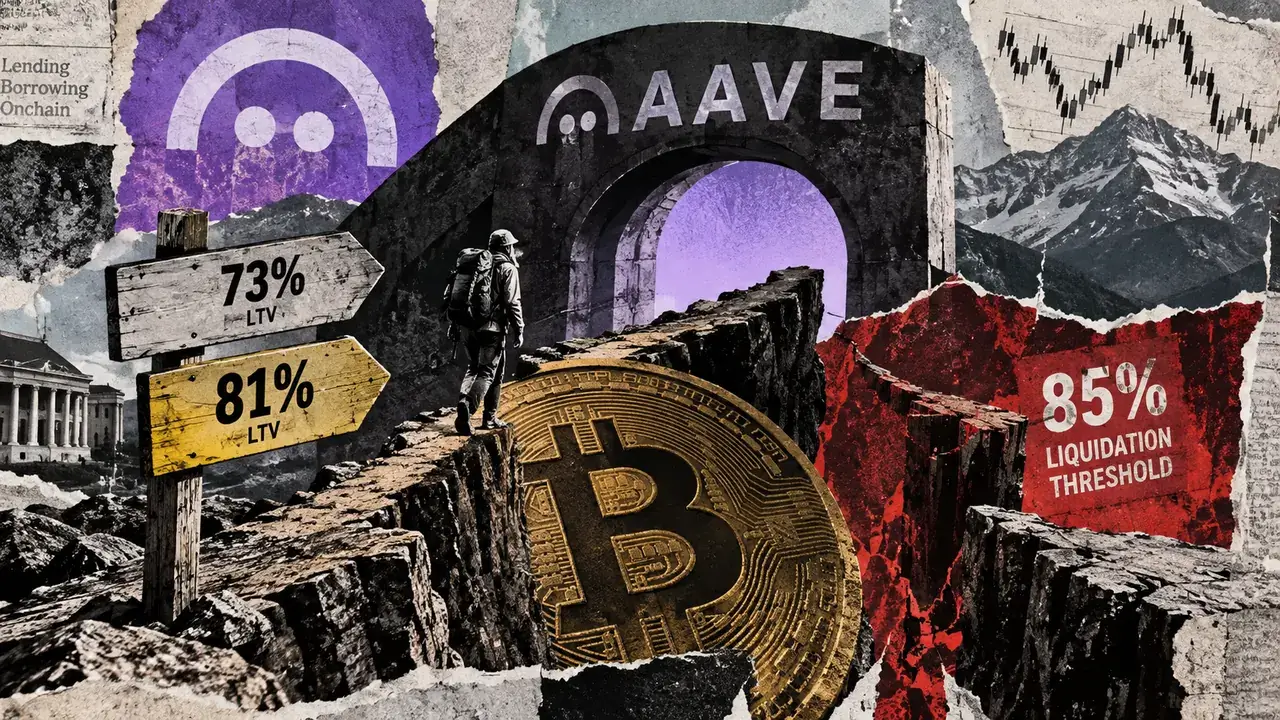
Narrowing price cushions leave Bitcoin loans vulnerable to 4.7% price dips as Aave weighs higher leverage
The plan would lift WBTC and cbBTC borrowing limits while shrinking the simplified maximum-leverage price cushion from 6.4% to 4.7%. The post Narrowing price cushions leave Bitcoin loans vulnerable to 4.7% price dips as Aave weighs higher leverage appeared…
Major DeFi Protocol Patches Vulnerability Before Funds Affected
A leading decentralised finance protocol has patched a smart-contract vulnerability identified by independent security researchers. The team says the flaw was fixed before any user funds were affected, and a bug-bounty reward was paid to the reporting…